Internal Control & SOX Testing
Test internal controls against SOX and policy checklists, flag gaps, and generate remediation plans with audit-ready evidence.
Skills in this bundle
Control Remediation Sentinel
Internal-control / SOX control-testing workpaper builder: reads a controls list, sizes samples by frequency and risk, and produces a control matrix, sampling plan, test worksheet template, deficiency-grading rubric, plus next-best-actions (actions.json) for high-risk controls.
Policy Lens
Deterministic policy red-flag clause analysis (severity filter + structure + score). No LLM. (Action Co-pilot: generates next-best-actions (actions.json), follow-up tasks and calendar reminders on top of the analysis — what to act on today.)
Quality Sentinel
Automated ISO 9001 and manufacturing quality standard compliance checker. Analyzes quality manuals, inspection records, and audit documents to identify non-conformities and generate prioritized remediation plans.
Regulatory Sentinel
Compliance check and internal control audit testing. Modes: check (document compliance against GDPR/SOC2/PCI-DSS/HIPAA/CSRC/CBRC/PBOC), audit (internal control testing with structured test report), fetch (regulatory docs), prompt (MD compliance prompts).
See it in action
MCP Nexus runs internal control and SOX testing against SOX and policy checklists, flags deficiencies, and generates remediation plans, taking control testing from days to hours with complete, reviewable evidence.
- Control testing runs automatically against SOX and policy checklists, with deficiencies flagged line by line.
- Policy and compliance checklists are built in, covering multiple control objectives.
- Deficiencies auto-generate remediation actions and owners, with a trackable closed loop.
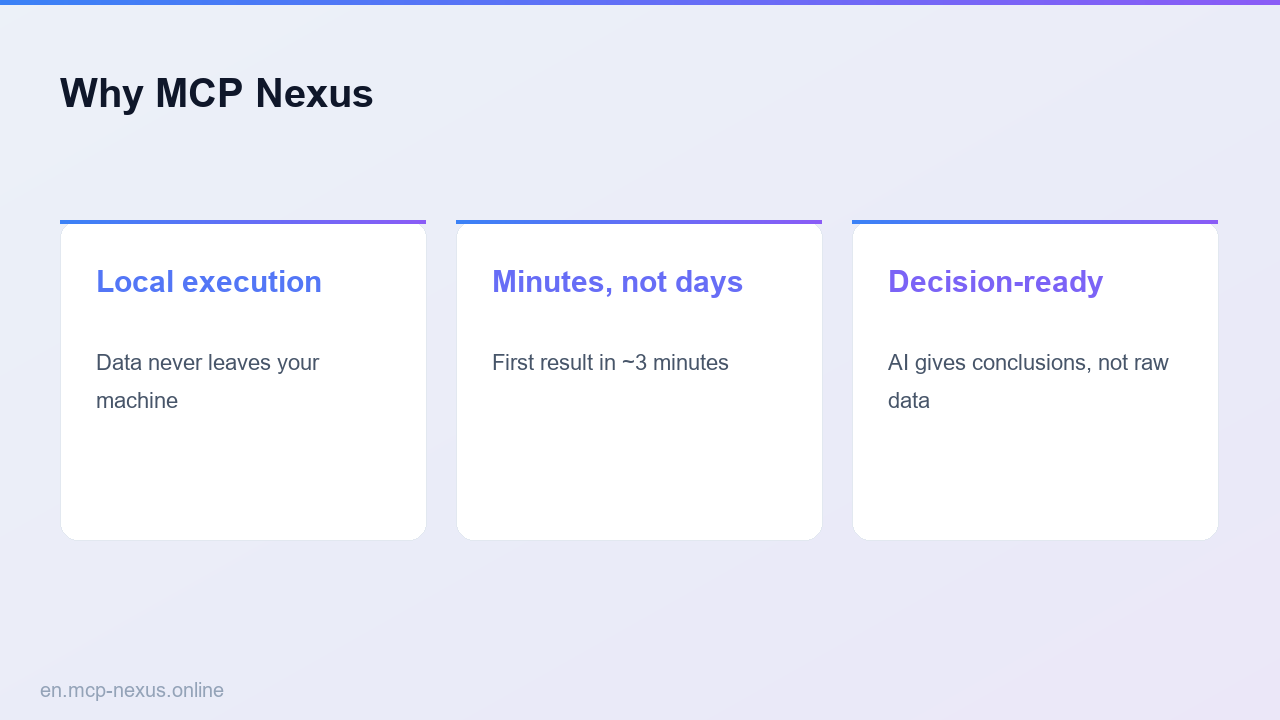
- Test papers and evidence are assembled on your machine; data never leaves your network.
- Exports control-test reports and remediation plans for review and reporting in minutes.
What is internal control & SOX testing with MCP Nexus
Internal control and SOX testing evaluates control design and operating effectiveness, identifies deficiencies, and drives remediation. MCP Nexus chains control-remediation-sentinel, policy-compliance-checker, quality-compliance-audit, compliance-check, and security-audit-toolkit to automate control testing, deficiency flagging, remediation recommendations, and reporting. It suits listed-company internal control, internal audit, and compliance teams, running fully on-premises.
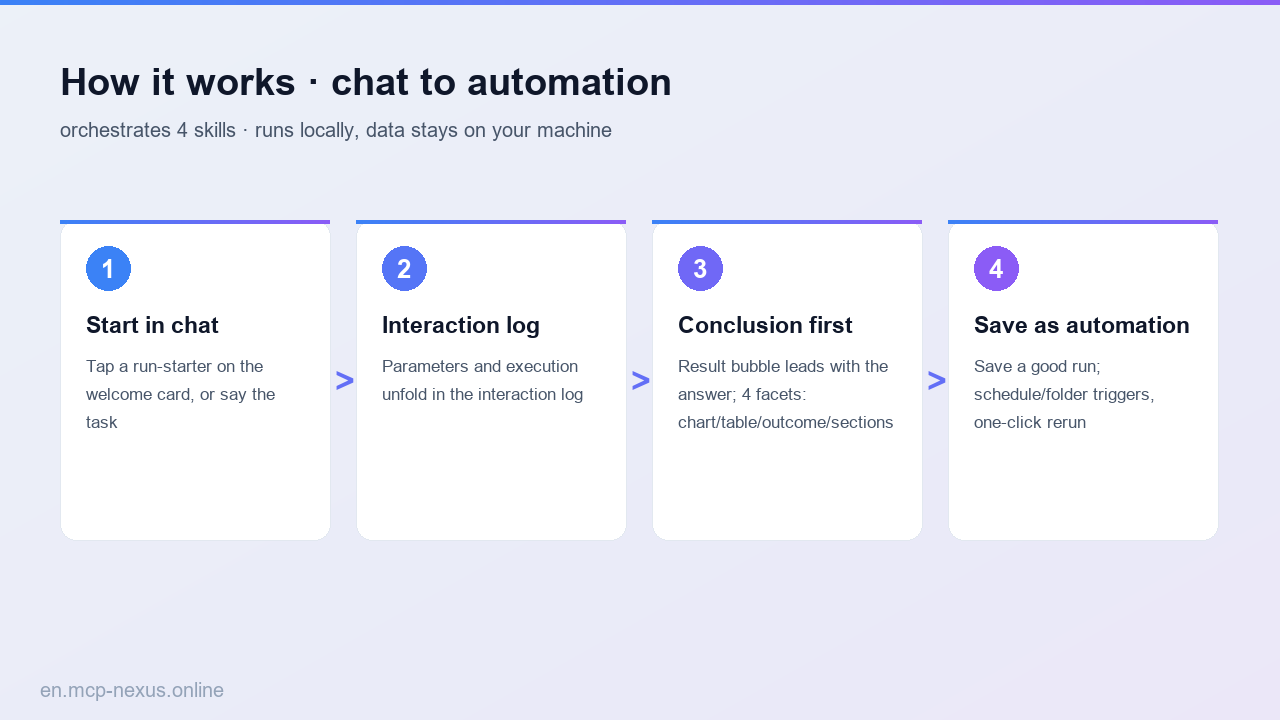
How it works
MCP Nexus vs alternatives
| MCP Nexus | Manual / Excel | Generic AI / Cloud tools | |
|---|---|---|---|
| Pricing | Free tier, metered by calls | Many internal-control hours | Per-seat plus per-volume fees |
| Local execution | Yes, data stays on-premises | Manual process | No, data leaves your network |
| Setup time | Minutes for first control | Days, experience-dependent | ~1 week integration and training |
Real use cases
FAQ
Which control frameworks and checklists are supported?
SOX control objectives and custom policy checklists, with your control matrix importable. Test dimensions and frequency are configurable across business and information-security controls.
How are deficiencies rated and remediated?
Deficiencies are rated by impact and likelihood, with remediation actions, owners, and deadlines auto-generated and status-tracked to closure.
Are test papers usable for audit?
Yes. Papers include control descriptions, test procedures, evidence, and conclusions with traceable evidence, exportable for internal and external audit review.
Can it work with our existing control matrix?
Yes. Importing your control matrix builds control-to-test mappings automatically, with no rebuild, keeping consistency with your internal-control system.
How is data security ensured?
Everything runs on your machine; control evidence and business data never leave the network, with private deployment and access control, meeting listed-company compliance.